Building a Data Enrichment Workflow for CRM and SaaS Applications
Customer records can lose value when important fields are missing, inconsistent, or out of date. Salesforce identifies completeness, accuracy, consistency, and timeliness as important dimensions of data quality. Its guidance also notes that disconnected and duplicate records can create an incomplete view of a customer.
For CRM and SaaS developers, one solution is to supplement existing records with structured information from external sources. A service providing sales intelligence, for example, may supply professional or company information that fills selected gaps. The goal is not to replace internal records. It is to add useful context while keeping the application’s primary database under its own control.
A Step-by-Step Guide to Building a Data Enrichment Workflow
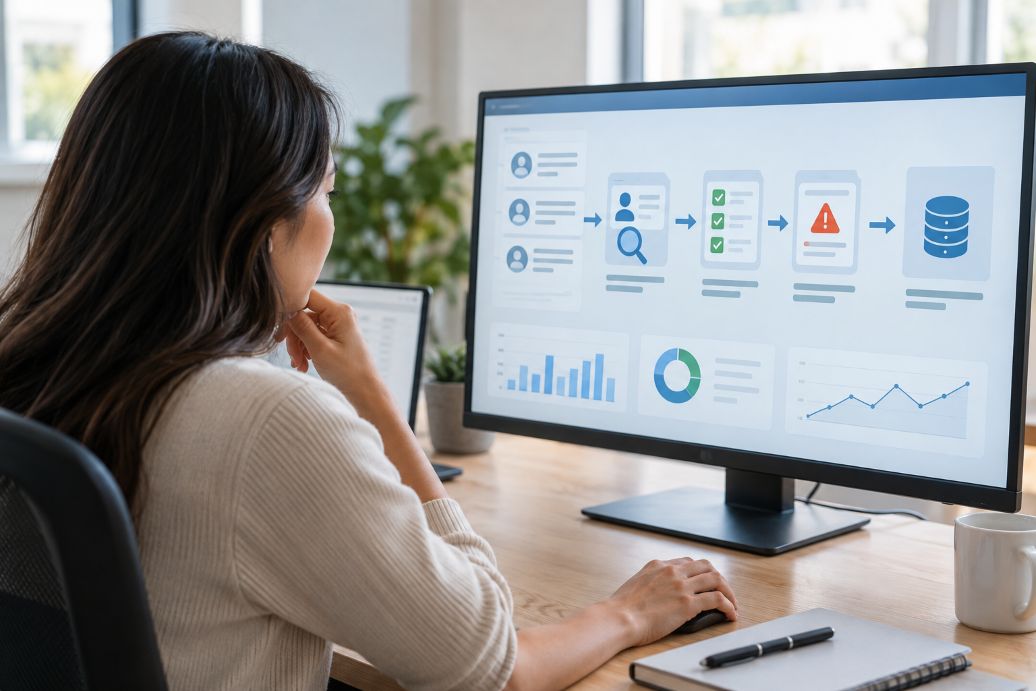
A reliable workflow needs more than an API connection. Developers must decide what information they need, how records will be matched, which responses are trustworthy, and when updates should be accepted. The following process provides a practical starting point.
1. Identify the Fields That Actually Need Enrichment
Start with the business problem rather than the available data. Review existing CRM records and identify fields that are consistently missing or becoming stale. These might include company size, industry, job title, professional role, location, or other relevant business attributes.
Salesforce recommends defining the fields required for each business use and measuring how many records have blanks in those fields. This creates a baseline before external information is introduced.
A narrow field list also reduces unnecessary processing. Avoid collecting information simply because an API makes it available. Each field should serve a defined application or business purpose.
2. Choose Appropriate Data Sources
Next, evaluate external providers based on the information your application needs. Consider coverage, update frequency, documentation, response structure, pricing, privacy requirements, and API limits.
EnvoAPI is one example of a professional-data service that developers may evaluate for this role. It should be assessed in the same way as any other provider. Test whether its available fields and matching options fit the application’s requirements before building it into production workflows.
It can also be useful to record where each enriched field originated. UK Information Commissioner’s Office guidance recommends keeping the source and status of personal information clear when managing accuracy.
3. Connect the API to Your Application
Once a source has been selected, create an integration layer between the provider and the CRM or SaaS application. Keep API credentials outside client-side code. Requests should pass through a controlled backend service where authentication, validation, logging, and usage limits can be managed.
The integration layer also gives developers one place to transform external responses into the application’s internal data format. This becomes especially useful if providers change later.
4. Match External Data to the Correct Record
Record matching is one of the most important parts of enrichment. A useful API response becomes harmful if it is attached to the wrong customer or company.
Use the strongest identifiers available. Depending on the dataset, these could include email addresses, company domains, external IDs, or combinations of name and company information. Avoid assuming that a name alone represents a unique person.
Salesforce uses matching and duplicate-management rules because several records can represent the same entity, while apparently similar records may represent different entities. Its tools support exact and fuzzy matching approaches.
5. Validate Every API Response
External data should never move directly into production records without validation. Check expected data types, required fields, permitted values, string lengths, and response structure.
OWASP recommends validating information from external sources as early as possible. Its guidance distinguishes syntactic checks, which confirm that data has the expected format, from semantic checks, which determine whether a value makes sense within its business context.
Developers should also decide what happens when incoming information conflicts with an existing value. A newer external value should not automatically overwrite a verified internal field. Confidence rules, timestamps, and source priority can help determine which version should be retained.
6. Plan for Errors and Failed Requests
External services will occasionally return errors, incomplete responses, or unavailable records. Build these possibilities into the workflow instead of treating every failed request as an exceptional event.
Use retry rules for temporary failures, but limit repeated requests. Log enough information to diagnose problems without exposing credentials or sensitive customer information. OWASP recommends centralized exception handling and warns against error responses that reveal sensitive system or account details.
A failed enrichment request should usually leave the original CRM record intact. The application can mark the attempt for review or retry rather than replacing valid information with blanks.
7. Store Enriched Data With Context
When validated information is accepted, store more than the final value where practical. Useful metadata can include the provider, enrichment date, match method, and last verification date.
This makes later maintenance easier. Teams can distinguish information entered directly by a customer from information supplied by an external source. The same principle can apply when information comes from less structured sources. For example, insights gathered through a developer feedback process may provide useful product context, but teams still need to document where that information came from and how it should be used. Clear source tracking also makes it easier to identify records that may need refreshing.
Keep Accuracy, Privacy, and Maintenance in the Workflow
Data enrichment is an ongoing process rather than a one-time cleanup. Company structures change. People change jobs. Providers update datasets, APIs, limits, and schemas. Applications therefore need monitoring and periodic testing.
Privacy deserves equal attention. UK Information Commissioner’s Office guidance on data protection emphasizes purpose limitation, data minimisation, accuracy, storage limitation, and security. These principles support collecting only information that has a clear purpose and keeping it no longer than necessary.
Rate limits should also shape the technical design. Instead of repeatedly enriching every CRM record, applications can prioritize new, incomplete, or sufficiently old records. Caching and scheduled jobs may further reduce unnecessary requests.
A strong enrichment workflow ultimately depends on controlled updates. Define the required fields first, select suitable sources, match records carefully, validate responses, handle failures safely, and preserve useful source metadata. With regular maintenance and privacy controls, enrichment can improve CRM and SaaS data without turning external information into an unchecked source of truth.